
junyamade

Open to cybersecurity & developer roles
I build IT. Then I secure IT. Software developer.

  • Johannesburg · open to remote
  • Everything here is live & on GitHub
  • Replies within 24h
Junya, cybersecurity analyst · software developer, holding a laptop
Junyacybersecurity analyst · software developer
0ATT&CK techniques run
0caught by default rules
0custom detections written
0incident write-ups

Flagship project

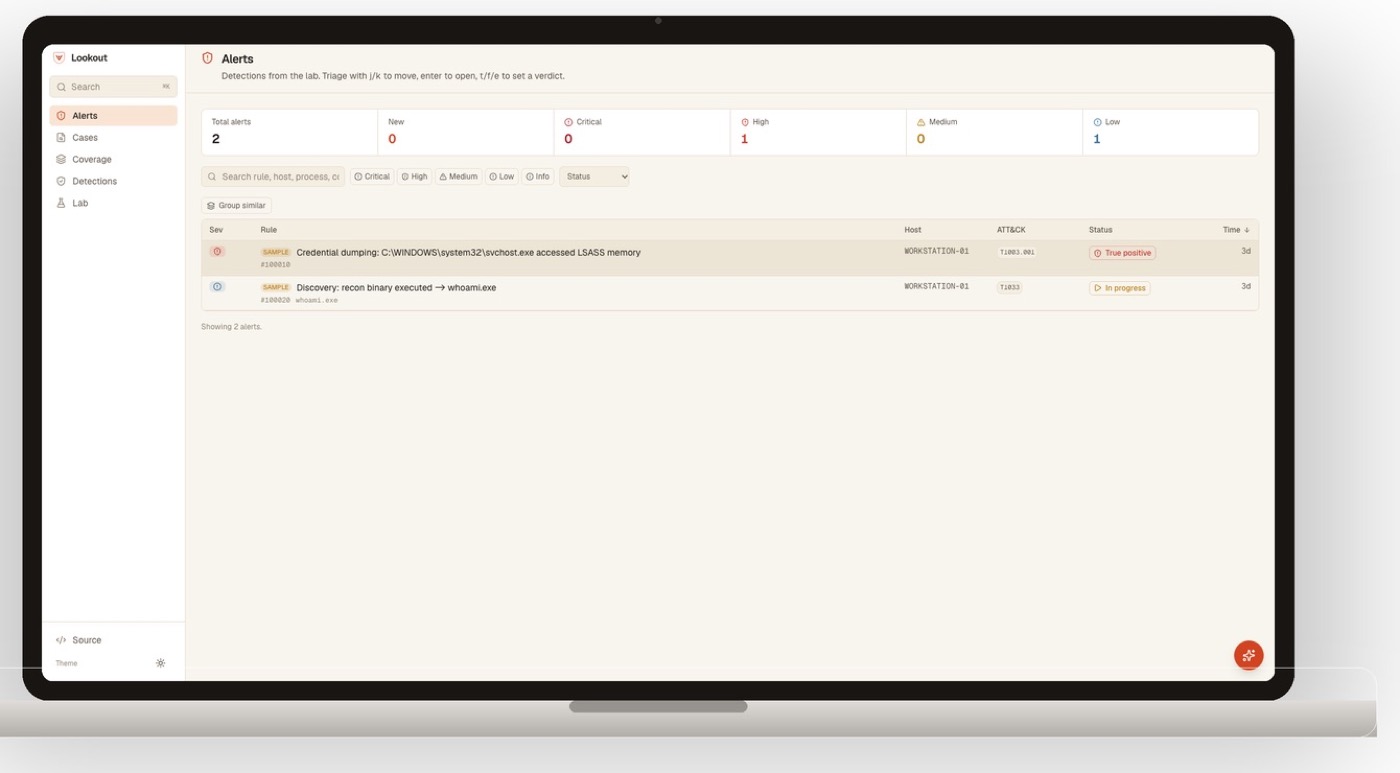
Lookout — a home SOC, triaged for real.

  • Lab Wazuh, Sysmon and Atomic Red Team on isolated VMs.
  • Finding Default rules caught 4 of 8 attacks — and missed credential dumping.
  • Fix Five custom detections and a triage console I built.
Lookout alert queue showing an LSASS credential-dumping alert marked true positive
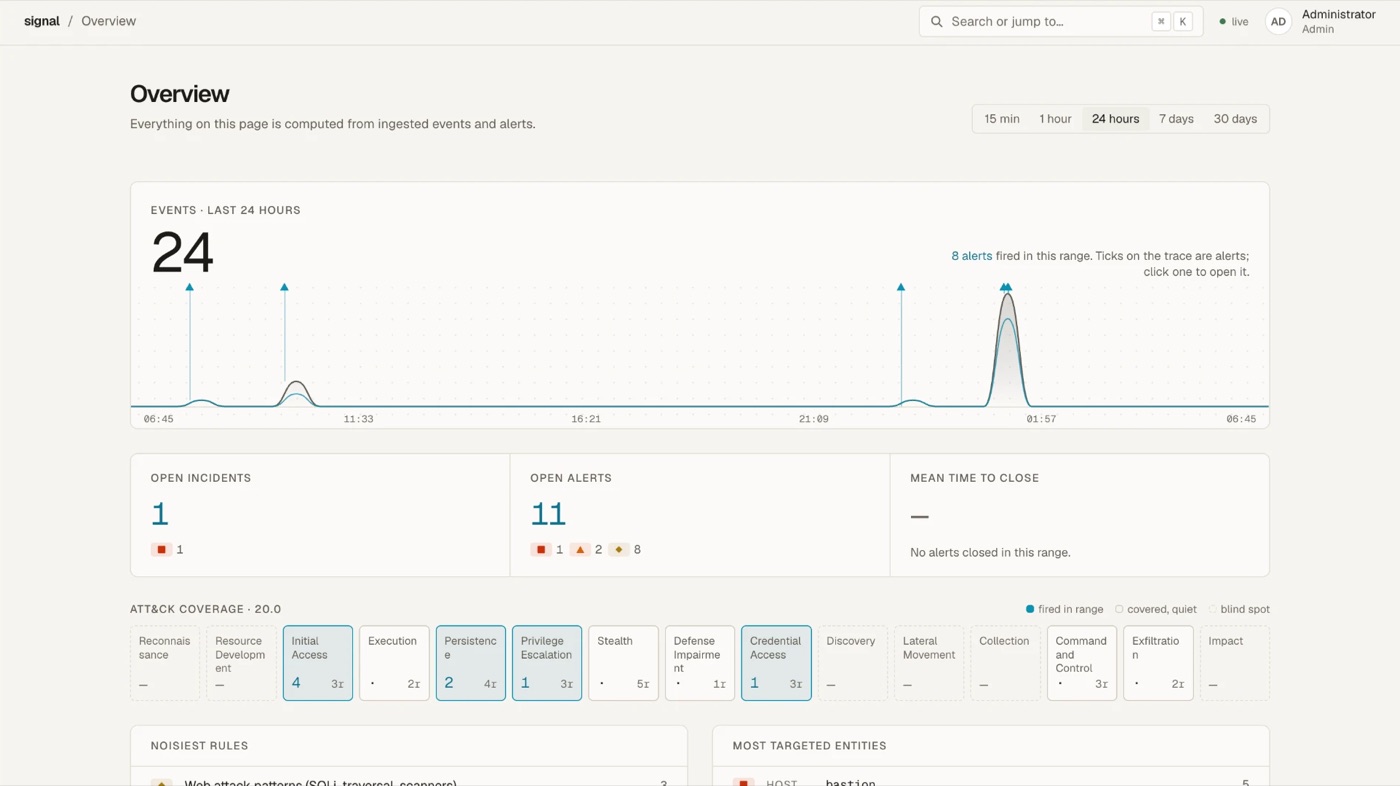
SIGNAL overview: event-rate trace with alert ticks, open incidents and ATT&CK coverage

Latest project

SIGNAL — a SIEM, built from the ground up.

  • Ingest Windows Security, Sysmon, Linux auth, web and Wazuh logs.
  • Detect 16 ATT&CK-mapped rules, each with a positive and a negative test.
  • Correlate Related alerts become one scored incident with an ATT&CK storyline.

The finding

What the defaults missed.

Eight ATT&CK techniques run against the lab, whether default Wazuh rules caught them, and the custom rule I wrote
TechniqueWhat it isDefault WazuhMy rule
T1033System owner / user discoveryDiscoveryMissed100020
T1059.001Encoded PowerShellExecutionCaughtnot needed
T1547.001Registry Run keyPersistenceMissed100030
T1053.005Scheduled taskPersistencePartial100050
T1136.001Create local accountPersistenceCaughtnot needed
T1003.001LSASS memory dumpCredential accessMissed100010
T1070.004File deletionDefense evasionCaughtnot needed
T1560.001Archive for exfil (makecab)CollectionMissed100040

Skills

Tools I use.

Security operations

  • Alert triage
  • Log analysis
  • MITRE ATT&CK mapping
  • True / false positive verdicts
  • Incident write-ups
  • Phishing analysis (SPF · DKIM · DMARC)

Detection & lab

  • Wazuh 4.14 (SIEM)
  • Sysmon + sysmon-modular
  • Custom Wazuh rules (XML)
  • Sigma-style detection rules
  • Atomic Red Team
  • Windows event logs · EVTX
  • Ubuntu server · UTM VMs

Secure engineering

  • Input validation (zod)
  • CSP · HSTS · security headers
  • Auth, CSRF & rate limiting
  • Webhook signature checks
  • Secret scanning (gitleaks)
  • Prompt-injection defences

Languages & tools

  • TypeScript · JavaScript
  • Python
  • SQL · Postgres
  • Java
  • Next.js · React
  • Git · GitHub Actions CI

Journey

From building to securing.

  1. 2026

    Shipped production software

    Client systems with logins, payments and personal data.

  2. Jun 2026

    Built PhishGuard

    A client-side phishing analyser.

  3. 2026

    Network Systems + Security+

    Boston City Campus · Security+ and TryHackMe SOC in progress.

  4. Oct 2026

    Built Lookout

    A home SOC lab with custom detections and triage.

  5. Oct 2026

    Built SIGNAL

    A self-hosted mini SIEM with ATT&CK-mapped detections and incident correlation.

  6. Next

    Joining a security team

    Johannesburg or remote.

References

What clients say.

Ntombi Mothoagae

Be Whole Care · Counselling

Verified client

He rebuilt our whole practice into one system — clients book and pay themselves now, and I run everything from one screen. I stopped chasing payments completely.

Mfundo Mayisa

DOOM IT · DJ & events

Verified client

My booking site is live on my own .co.za domain and it looks exactly like my brand. Enquiries come straight to my phone — bookings got easier immediately.

BN Dreamlight

Solar · water · electrical

Verified client

Our services and prices are laid out clearly and quote requests come straight to WhatsApp. The site makes us look as professional as we actually are.

Tshepo M.

Small business owner

Verified client

Fast, and he explains things without the jargon. Took a bit longer than I expected because I was slow sending photos, but the result speaks for itself.

Hiring?

Let’s talk.

Happy to walk through Lookout live.