
 Security
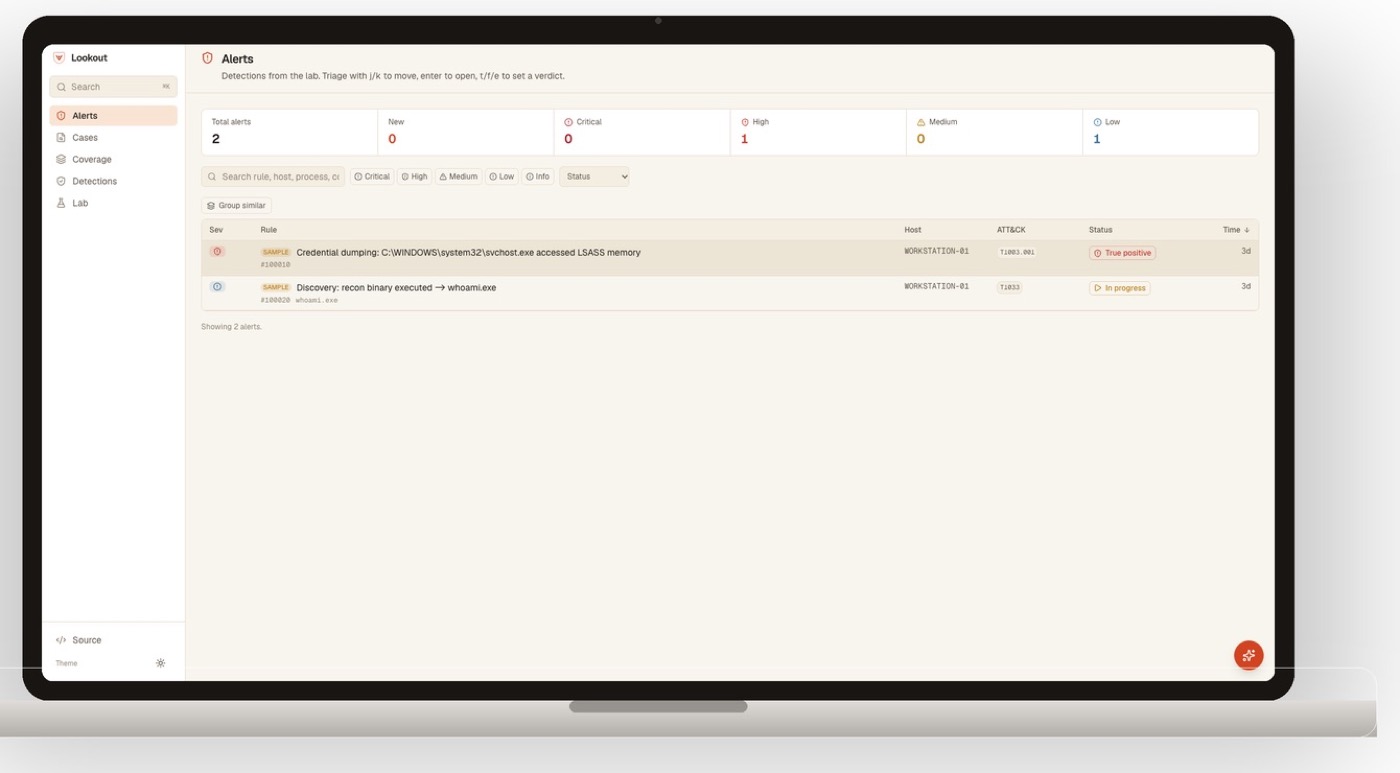
Lookout
Home SOC lab · AI-assisted triage
Real attacks, real logs, five custom detections and a triage console.
Security
SOC work end to end: attack, collect, detect, triage and report — in my own lab and in a SIEM I built. Everything below is live or on GitHub.
SecurityHome SOC lab · AI-assisted triage
Real attacks, real logs, five custom detections and a triage console.
 Security
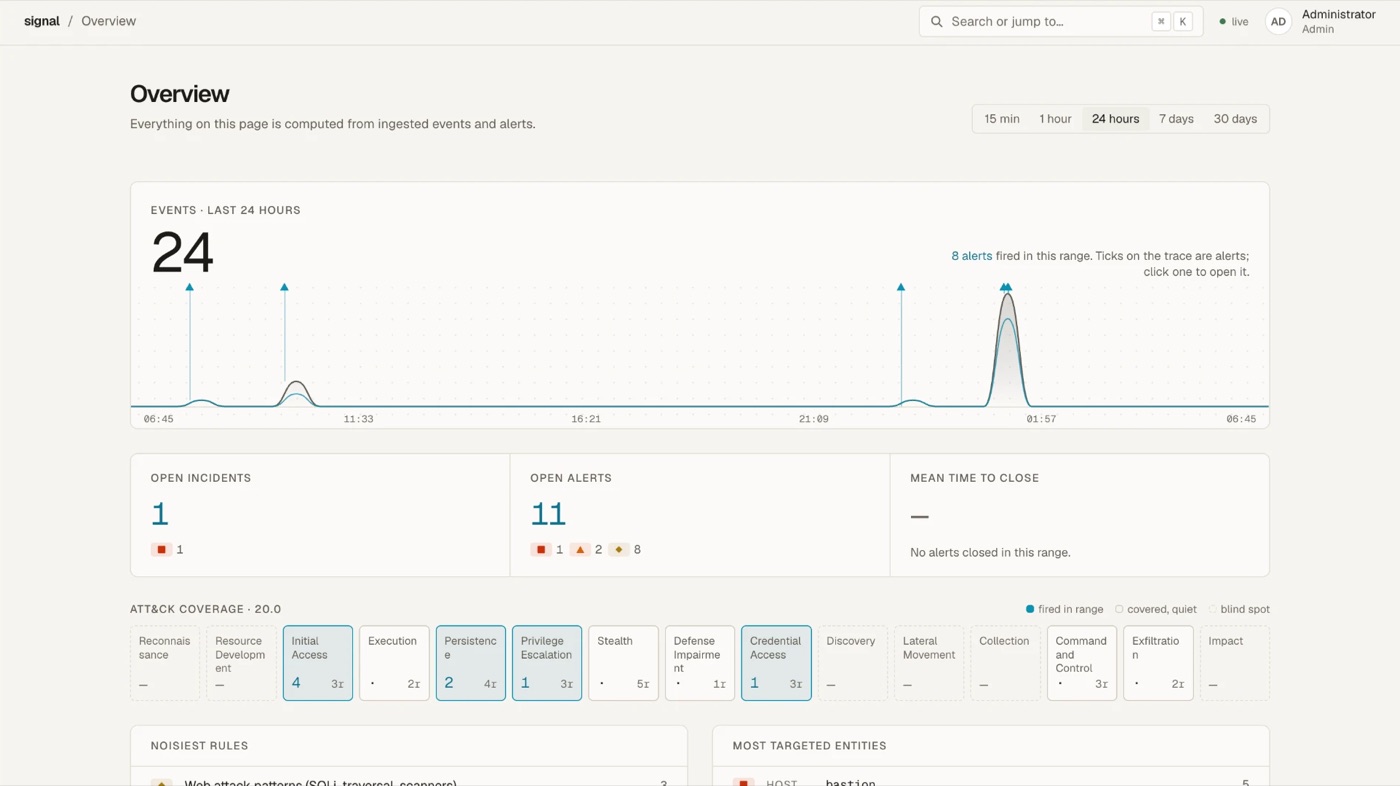
Self-hosted mini SIEM
Ingests Windows, Sysmon and Linux logs, runs 16 ATT&CK-mapped rules and correlates alerts into scored incidents.
 Security
Detection coverage
The out-of-the-box Wazuh ruleset against Atomic Red Team — and the rules I wrote to close the gaps.
| Technique | What it is | Default Wazuh | My rule |
|---|---|---|---|
T1033 | System owner / user discoveryDiscovery | Missed | 100020 |
T1059.001 | Encoded PowerShellExecution | Caught | not needed |
T1547.001 | Registry Run keyPersistence | Missed | 100030 |
T1053.005 | Scheduled taskPersistence | Partial | 100050 |
T1136.001 | Create local accountPersistence | Caught | not needed |
T1003.001 | LSASS memory dumpCredential access | Missed | 100010 |
T1070.004 | File deletionDefense evasion | Caught | not needed |
T1560.001 | Archive for exfil (makecab)Collection | Missed | 100040 |
Method and false-positive notes in the Lookout case study.
Security skills
How I think
01
You can’t alert on what you don’t collect — check the endpoint, not just the SIEM.
02
False positives are where tuning starts. I document them.
03
Validated, never executed. I make the final call.
Training
CompTIA Security+ (SY0-701) and TryHackMe SOC Level 1 in progress — every lab lesson is mapped to a Security+ domain.